
Internal tool - Cloud-security and cost visibility across projects
Giving a small engineering team centralized cloud-security and cost visibility. Internal tool.
- Client
- BeeNex — BeeSecurity
- Year
- Service
- Internal tools, Cloud security, Observability, Cost visibility
- Engagement
- Internal tool
The Challenge
A multi-project cloud environment needed a shared view of IAM, credentials, billing and operational anomalies.
The Approach
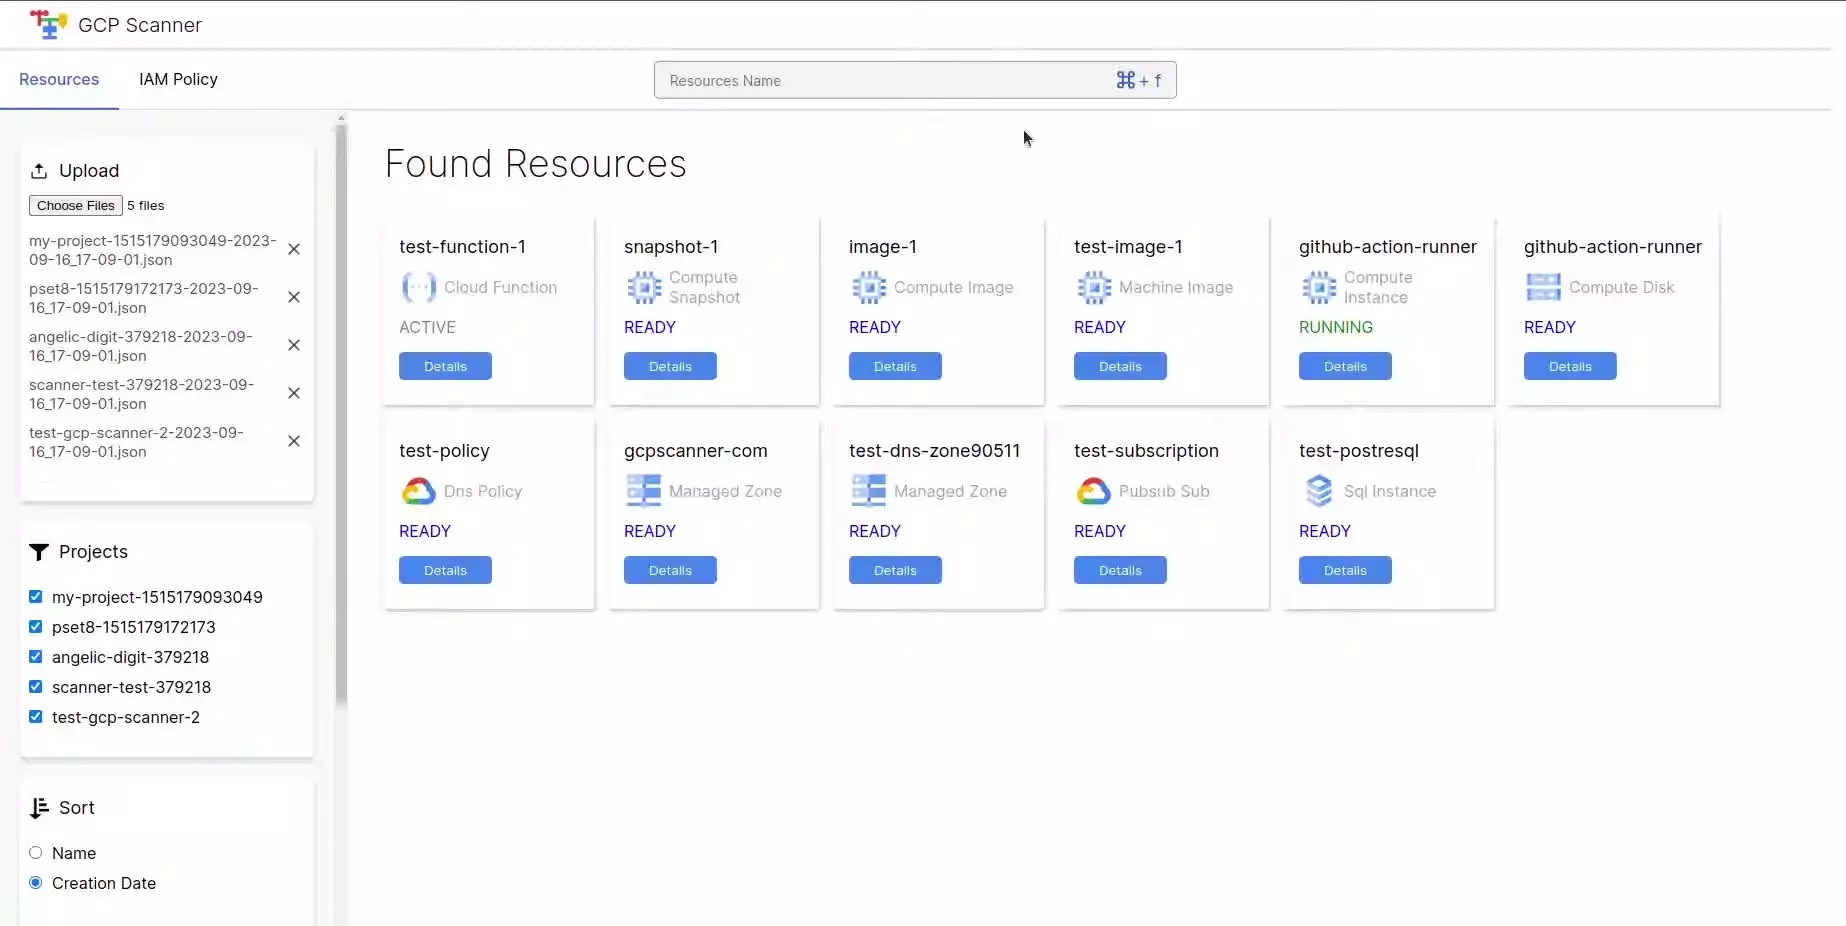
BeeNex built an internal dashboard and scan/reporting workflow for documented cloud-security and cost checks. The application combines IAM/credential hygiene, billing anomalies, API/quota visibility and alerts, while coverage review identifies where it should expand.
Capabilities
- IAM/credential hygiene
- Billing monitoring
- Spend anomaly detection
- API usage views
- Quota visibility
- Security posture score
- Scan scheduling
- Dashboard alerts
- Telegram reporting
- Coverage review and expansion
Workflow
- Discover projects/assets
- Run defined checks
- Aggregate findings and costs
- Display dashboard
- Send alerts
- Review coverage gaps
- Repeat scans
- Python
- FastAPI
- Next.js
- Docker
- Google Cloud
- Workload Identity Federation
- Cloud Asset Inventory
- Telegram
Outcome
The documentation and scan emails establish an internal monitoring application, including one reported scan across 46 projects. The case describes operational visibility and evolving check coverage.